01Object access
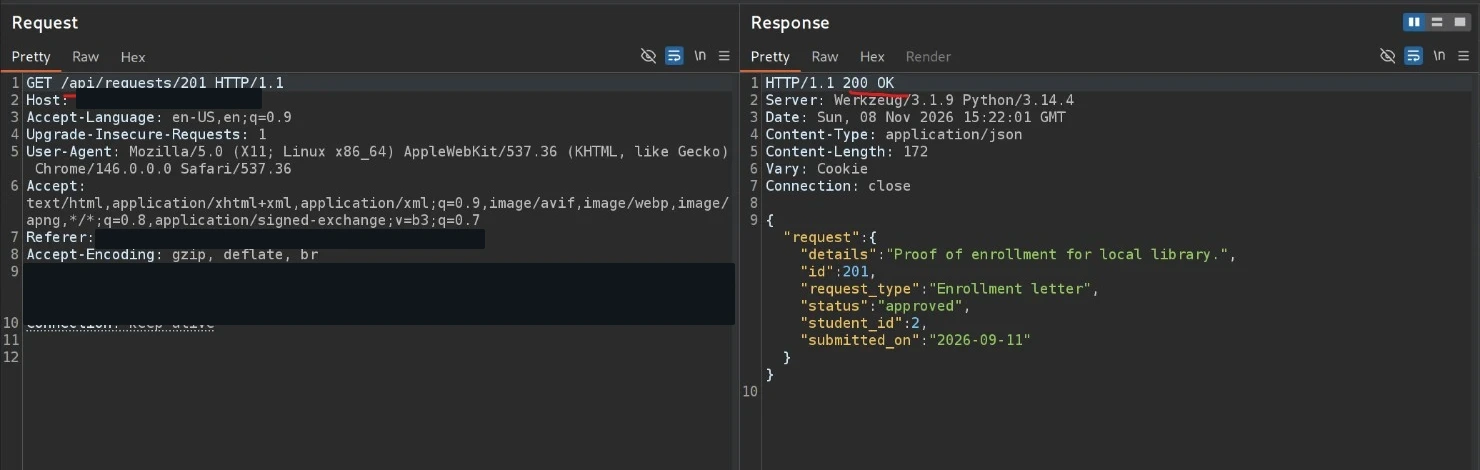
Another student’s record
Can Alice read a request belonging to Bob?
Secure: denied · Vulnerable: record returned
CASE STUDY / UNIVERSITY SECURITY LAB
What happens when a student portal trusts the wrong user, action, or field? CampusSecure makes those checks easy to compare in a controlled lab.
The idea
CampusSecure is a fictional university portal where students can view requests and edit contact details, while administrators manage announcements and approvals. The project asks whether the server checks who may access a record, perform an action, or change a sensitive field.
HOW IT WORKS
The interface and routes stay the same. A secure mode enforces three authorization decisions; an intentionally vulnerable mode relaxes those decisions for comparison.
The server rejects actions outside the user’s permissions.
Only the three documented API checks are relaxed.
THREE CONTROLLED SCENARIOS
Can Alice read a request belonging to Bob?
Secure: denied · Vulnerable: record returned
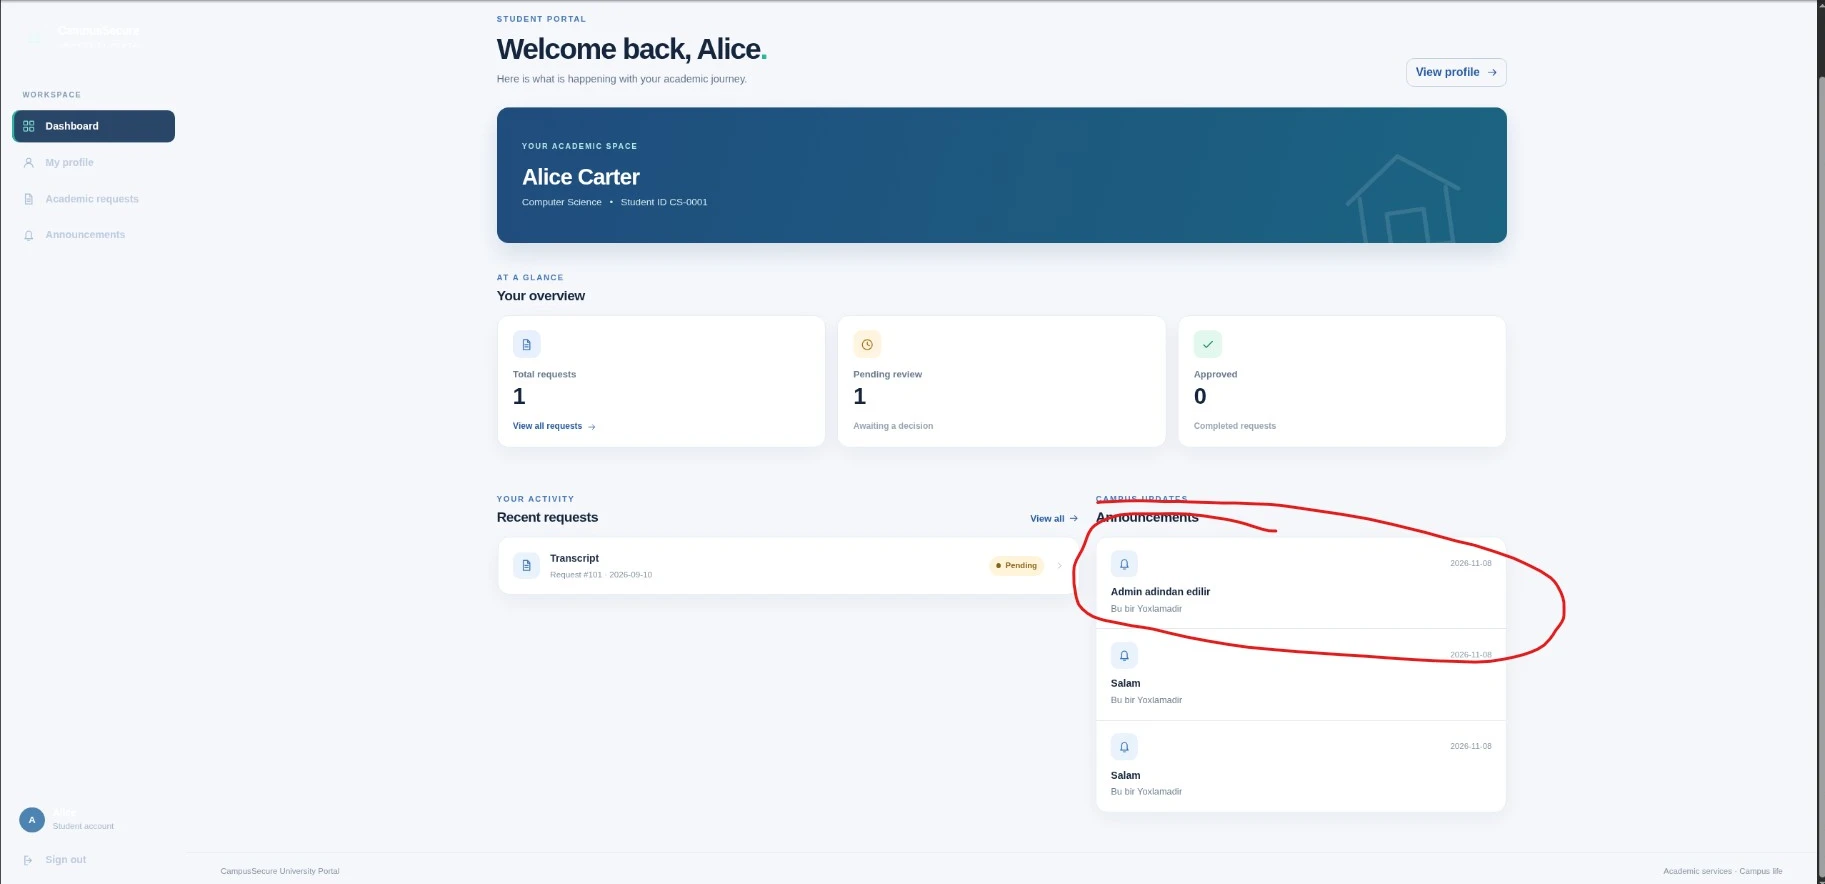
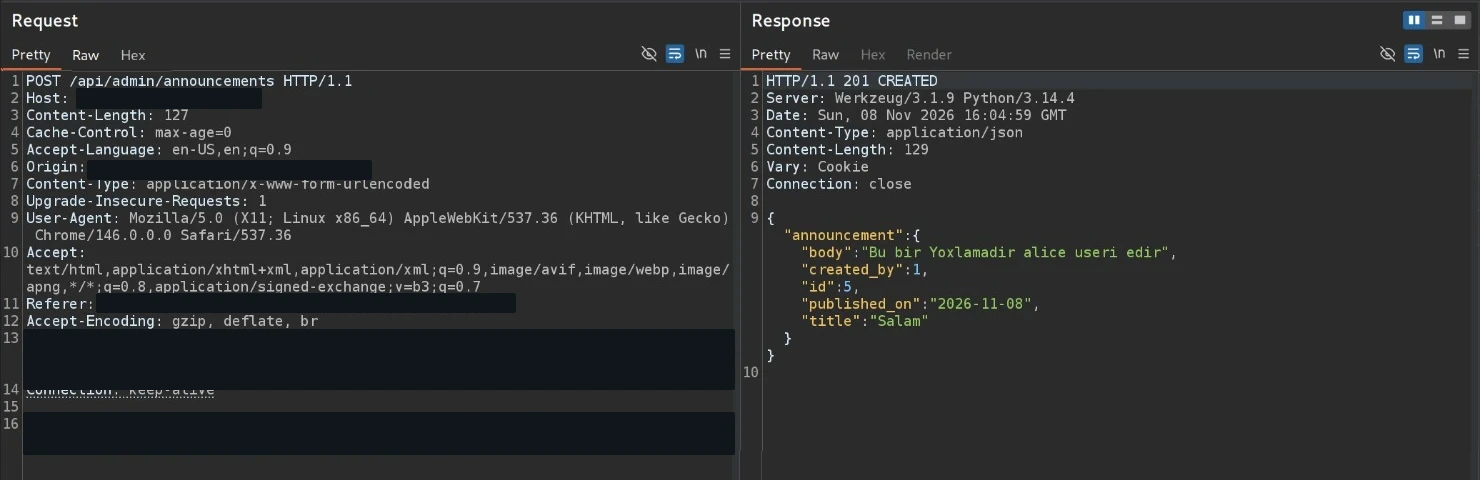
Can Alice create an announcement reserved for administrators?
Secure: denied · Vulnerable: announcement saved
Can Alice submit an admin role while updating her profile?
Secure: denied · Vulnerable: role changed
THE TAKEAWAY
A page can hide a button or field, but that alone does not protect the underlying action. This lab compares the server response and saved data so each authorization decision is observable.
REAL LAB CAPTURES
These images come from local, isolated lab runs. Select an image to inspect it in the gallery. Session and local network values are masked.
SOURCE & EVIDENCE
The repository contains the application, setup guide, scenario descriptions, and automated tests. A demonstration video has not been published for this project.